Unified Network Security Solution Design Guide
A comprehensive enterprise-grade network security solution covering design, selection, and implementation guidelines for small and medium-sized enterprises.
System Overview
This system provides a practical, compliance-based proactive defense framework for small and medium-sized enterprise networks. The core objective is to elevate the security posture of customer networks to industry-recommended standards through a closed-loop process of "standard formulation - compliance detection - protection reinforcement" and continuous operations and maintenance.
The system is designed for organizations with 50-2,000 employees that have independent network boundaries and data centers. It integrates multiple security components including Next-Generation Firewalls (NGFW), Intrusion Prevention Systems (IPS), Web Application Firewalls (WAF), Endpoint Detection and Response (EDR), and Security Information and Event Management (SIEM) platforms to provide comprehensive network security protection.
Core Value Propositions
Stable & Reliable
Ensures uninterrupted security services through device redundancy, link aggregation, and health monitoring.
Maintainable
Reduces operational complexity with integrated management platforms and provides clear compliance reports with remediation guidance.
Scalable
Modular design supports smooth expansion from basic firewall and EDR to complete advanced threat defense.
Cost-Optimized
Reduces business interruption and data breach losses through preventive protection, optimizing total cost of ownership.
System Architecture
The system architecture is designed with a three-layer approach: Display Layer (top), Analysis & Control Layer (middle), and Protection & Collection Layer (bottom). This layered architecture ensures clear separation of concerns while enabling seamless integration and data flow between components.
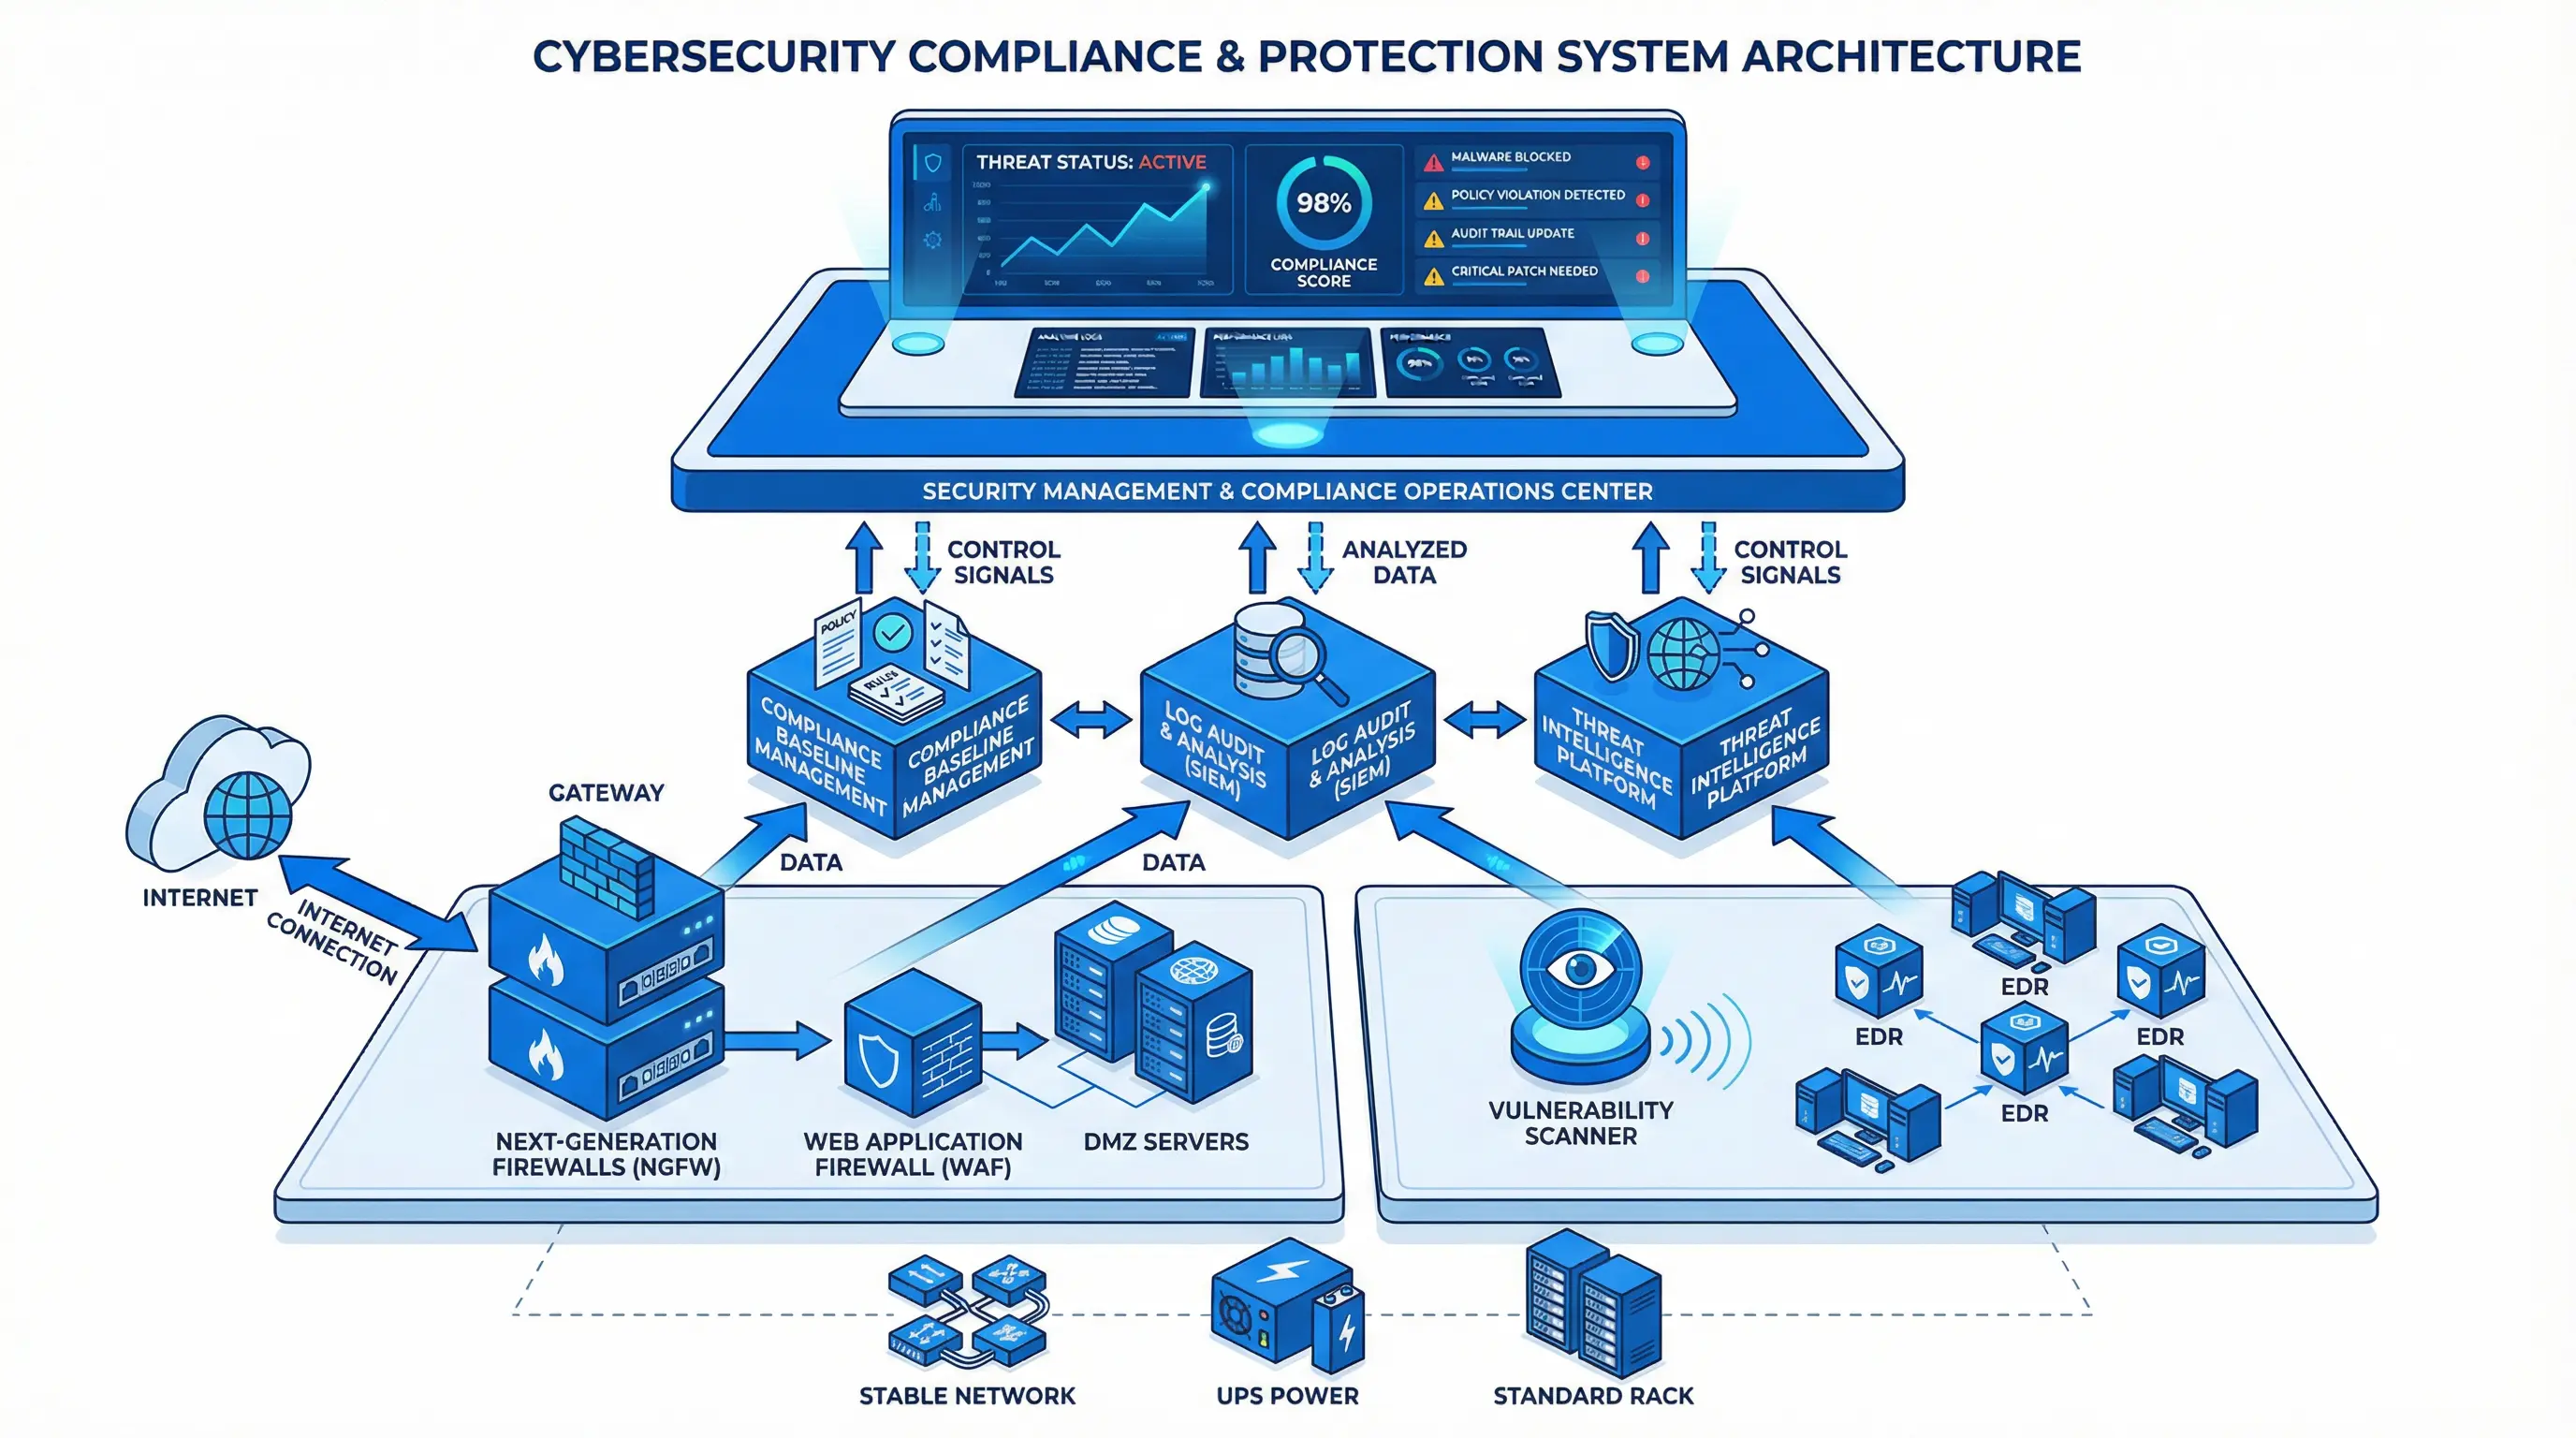
The Display Layer provides a unified security management and compliance operations center with visualization dashboards showing threat status, compliance scores, and event alerts. The Analysis & Control Layer includes core modules for compliance baseline management, log audit and analysis (SIEM), and threat intelligence platforms. The Protection & Collection Layer executes real-time defense through access control, intrusion prevention, and virus filtering while collecting comprehensive data from all network segments.
Main Functions
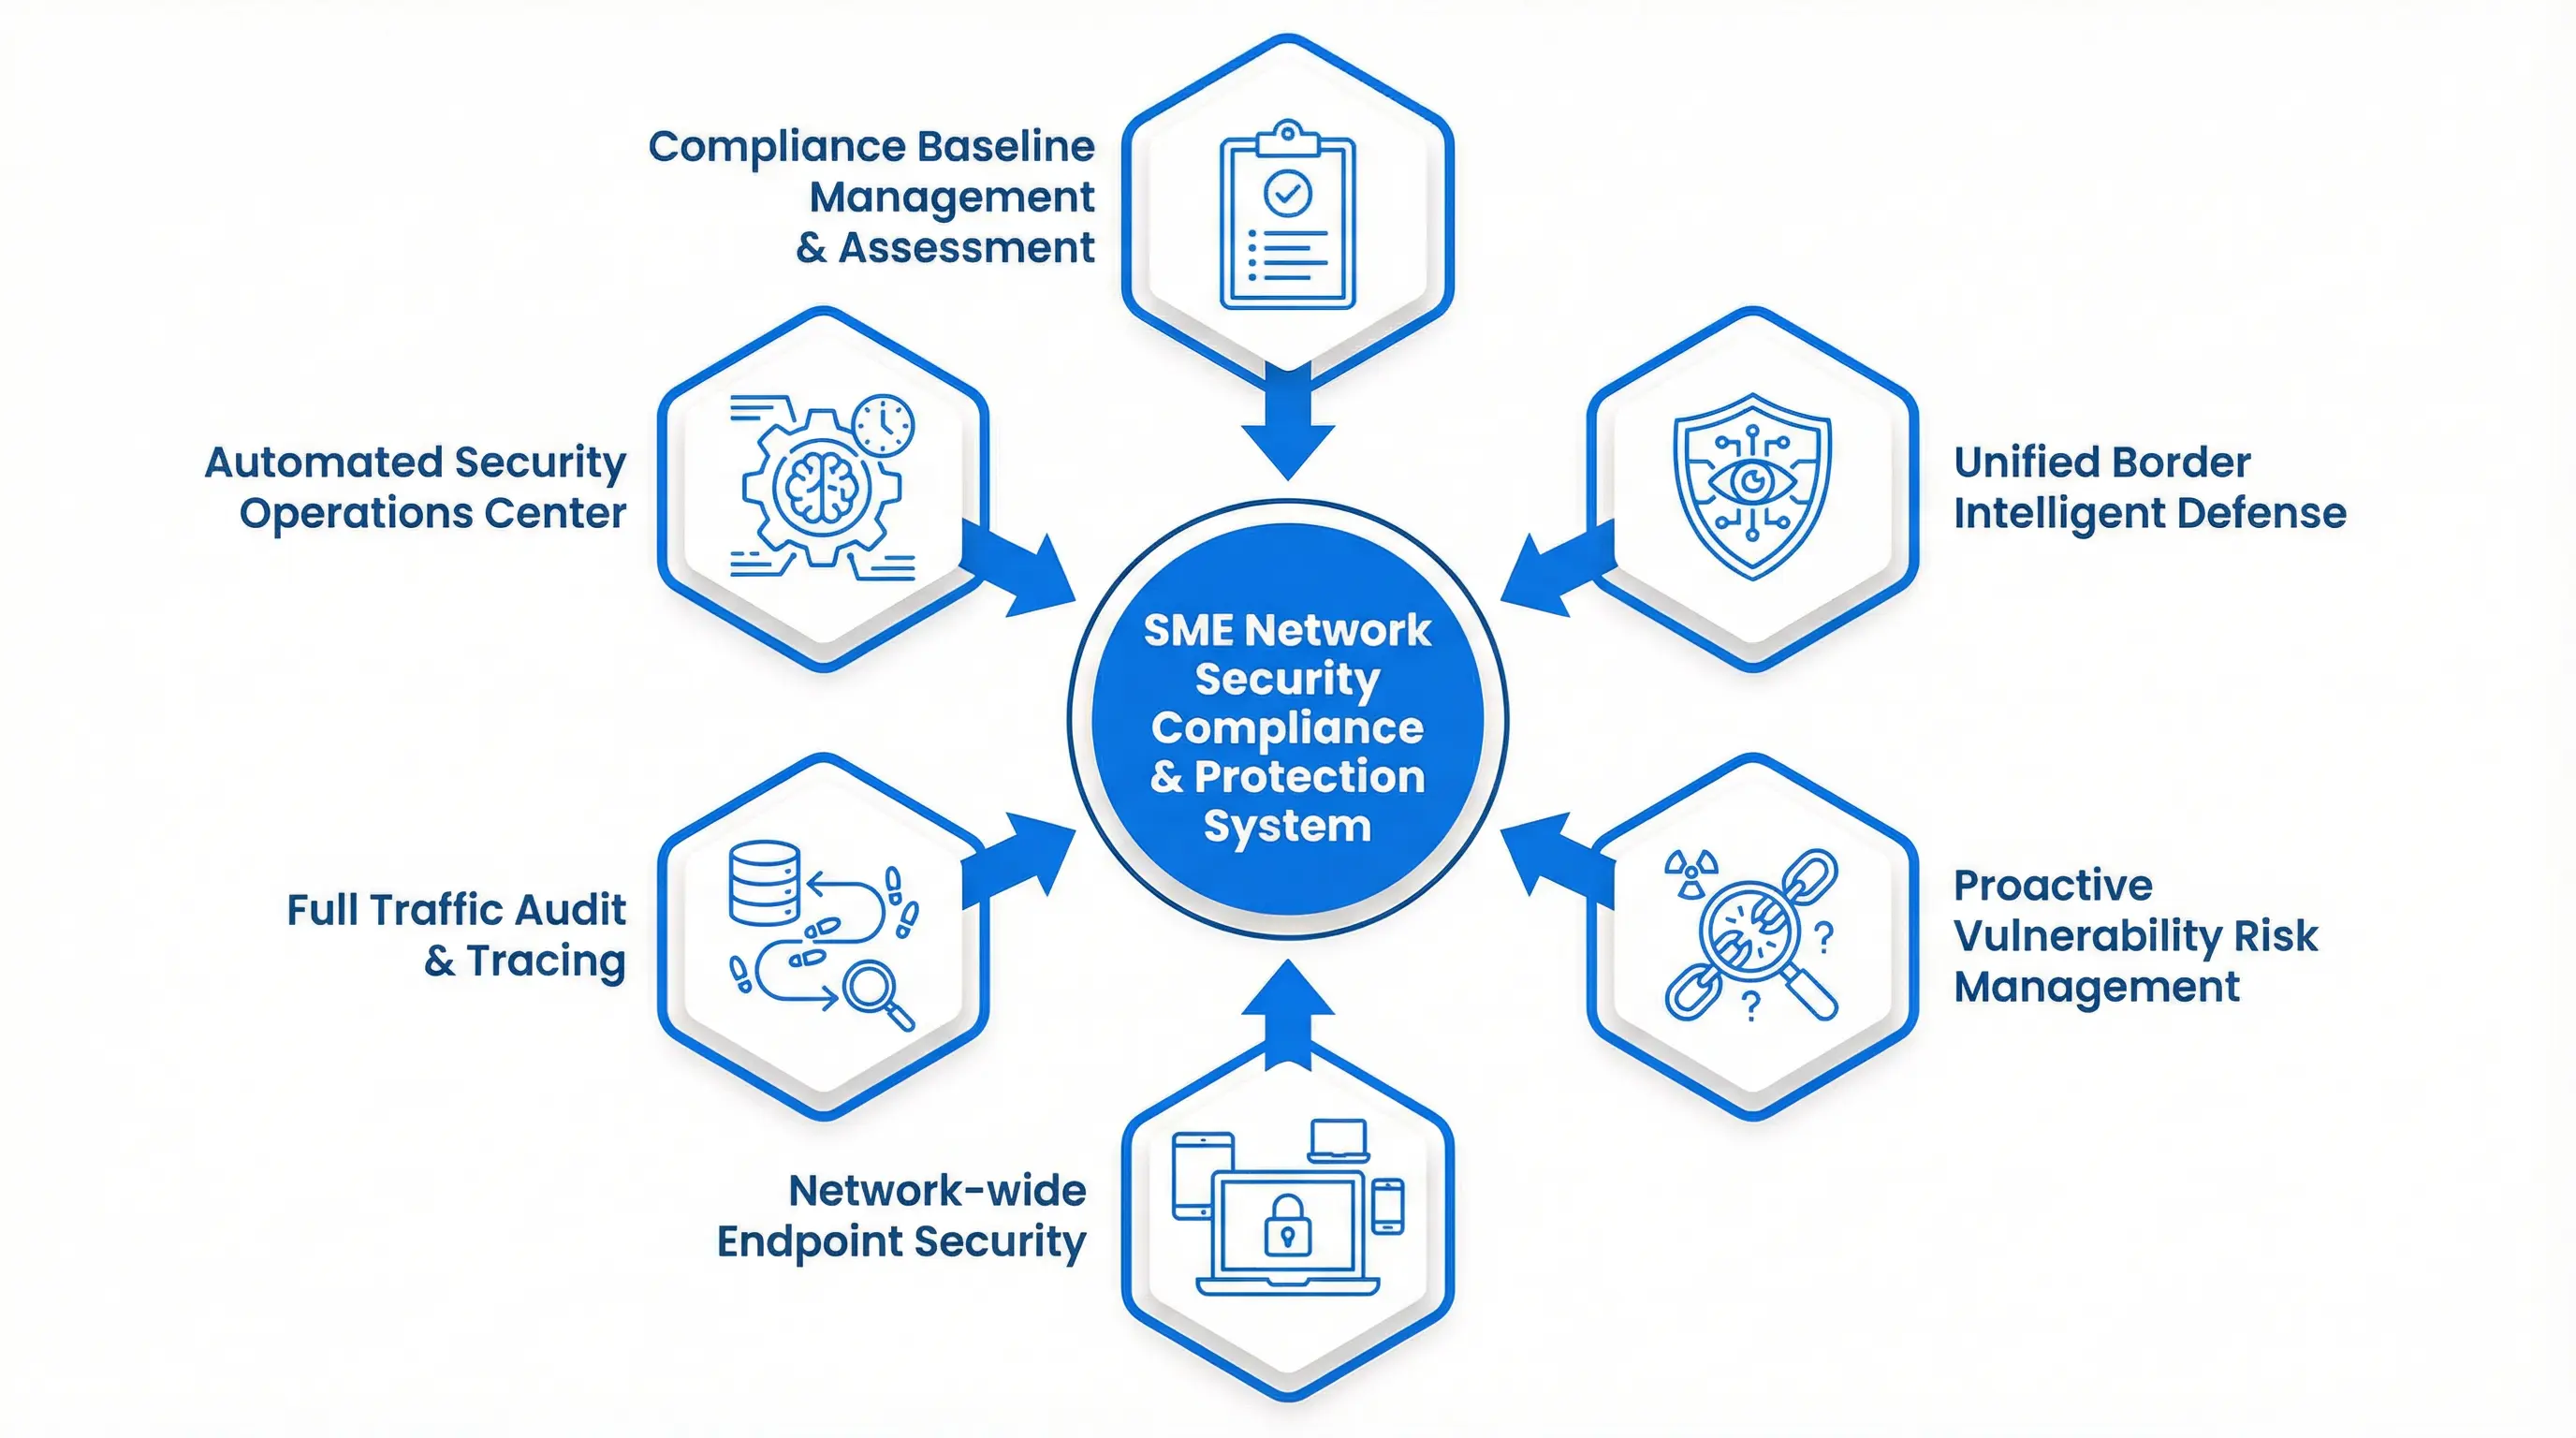
The system provides six major functional modules that work together to deliver comprehensive network security protection and compliance management capabilities.
Key Capabilities
- Compliance Baseline Management & Assessment: Built-in knowledge base of SME Network Security Recommended Standards with automated compliance checking and gap analysis reporting.
- Unified Border Intelligent Defense: Integrated NGFW, IPS, and AV capabilities at the network boundary for unified protection and fine-grained access control based on applications, users, and content.
- Web Application Deep Protection: WAF capabilities defending against SQL injection, XSS, CC attacks, and other web-layer threats to protect public-facing services.
- Network-wide Endpoint Security: EDR deployment on all endpoints providing virus scanning, behavior monitoring, threat tracing, and rapid response capabilities.
- Full Traffic Audit & Tracing: SIEM platform collecting logs and events from network devices, security devices, servers, and endpoints for correlation analysis, storage, and audit.
- Automated Security Operations: Closed-loop "monitor-analyze-respond-optimize" process with playbook-driven automation for 24/7 security operations.